SSH 基础
SSH(Secure Shell)是管理 Linux 服务器最核心的工具。本文介绍 OpenSSH 的安装配置、密钥管理和安全最佳实践。
安装 OpenSSH
安装服务端
# 安装 OpenSSH 服务器
sudo apt update
sudo apt install openssh-server -y

# 启动并设置开机自启
sudo systemctl enable --now ssh

# 查看运行状态
sudo systemctl status ssh

# 查看 SSH 监听端口
ss -tlnp | grep ssh
安装客户端
# Ubuntu 默认已安装客户端,如未安装:
sudo apt install openssh-client -y
SSH 密钥管理
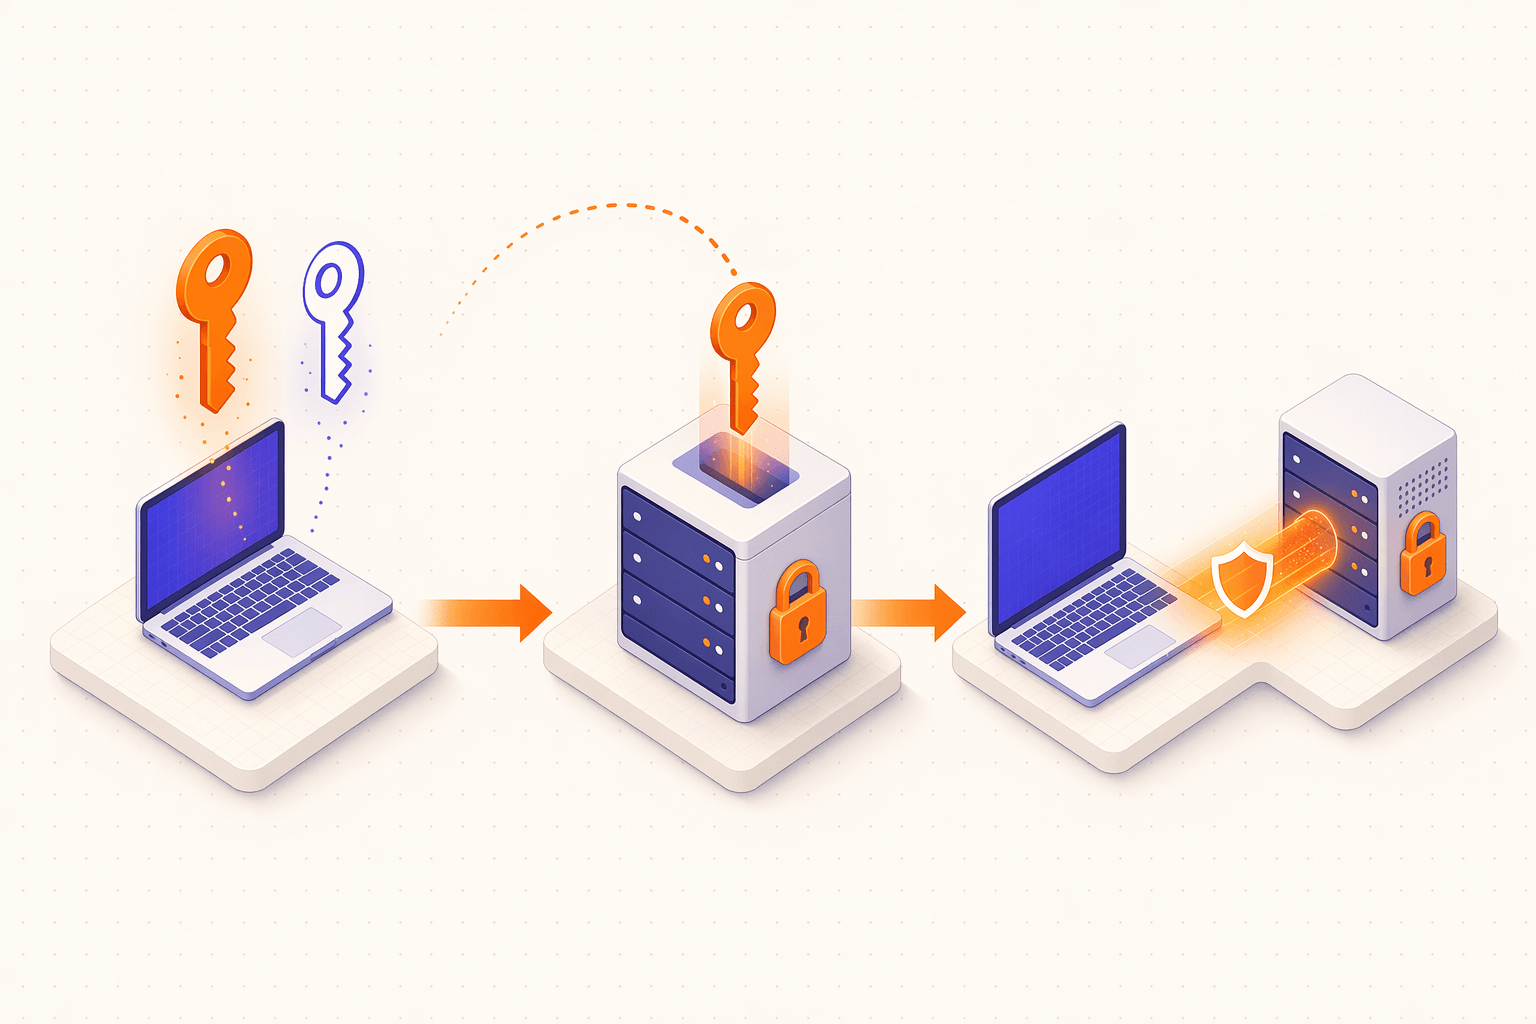
1生成密钥对
ssh-keygen -t ed25519 -C "you@host",私钥留本地,公钥可外传。
2推送公钥
ssh-copy-id user@server 把公钥写到远端 ~/.ssh/authorized_keys。
3建立安全会话
ssh user@server 用私钥协商,整个会话加密;建议禁用密码登录。
密钥认证比密码认证更安全、更方便。
生成密钥对
# 生成 Ed25519 密钥(推荐)
ssh-keygen -t ed25519 -C "your_email@example.com"

# 生成 RSA 4096 位密钥(兼容性更好)
ssh-keygen -t rsa -b 4096 -C "your_email@example.com"

# 指定文件名
ssh-keygen -t ed25519 -f ~/.ssh/id_myserver -C "myserver key"
密钥生成后:
- 私钥:
~/.ssh/id_ed25519(严格保密) - 公钥:
~/.ssh/id_ed25519.pub(可以分发)
复制公钥到服务器
# 方法 1:使用 ssh-copy-id(推荐)
ssh-copy-id -i ~/.ssh/id_ed25519.pub user@server-ip

# 方法 2:手动复制
cat ~/.ssh/id_ed25519.pub | ssh user@server-ip "mkdir -p ~/.ssh && chmod 700 ~/.ssh && cat >> ~/.ssh/authorized_keys && chmod 600 ~/.ssh/authorized_keys"

# 方法 3:如果已有公钥内容,在服务器上直接添加
echo "ssh-ed25519 AAAA... your_email@example.com" >> ~/.ssh/authorized_keys
管理 SSH Agent
# 启动 SSH Agent
eval "$(ssh-agent -s)"

# 添加密钥到 Agent
ssh-add ~/.ssh/id_ed25519

# 查看已加载的密钥
ssh-add -l

# 删除所有已加载的密钥
ssh-add -D
SSH 客户端配置
编辑 ~/.ssh/config 简化连接:
# ~/.ssh/config 示例
Host myserver
    HostName 192.168.1.100
    User ubuntu
    Port 22
    IdentityFile ~/.ssh/id_myserver

Host production
    HostName prod.example.com
    User deploy
    Port 2222
    IdentityFile ~/.ssh/id_prod
    ForwardAgent yes

Host jump
    HostName jump.example.com
    User admin

# 通过跳板机连接内网服务器
Host internal
    HostName 10.0.0.50
    User admin
    ProxyJump jump

# 所有主机的默认配置
Host *
    ServerAliveInterval 60
    ServerAliveCountMax 3
    AddKeysToAgent yes
    Compression yes
使用配置后的连接方式:
# 直接用别名连接
ssh myserver

# 等同于
ssh -i ~/.ssh/id_myserver -p 22 ubuntu@192.168.1.100
SSH 服务端配置
主配置文件为 /etc/ssh/sshd_config。
安全加固配置
# 备份原始配置
sudo cp /etc/ssh/sshd_config /etc/ssh/sshd_config.bak

# 编辑配置
sudo nano /etc/ssh/sshd_config
推荐的安全配置项:
# /etc/ssh/sshd_config

# 修改默认端口(降低扫描风险)
Port 2222

# 仅监听指定地址
ListenAddress 0.0.0.0

# 禁用 root 远程登录
PermitRootLogin no

# 禁用密码认证(确保已配置密钥登录)
PasswordAuthentication no

# 禁用空密码
PermitEmptyPasswords no

# 启用公钥认证
PubkeyAuthentication yes

# 限制最大认证尝试次数
MaxAuthTries 3

# 限制最大并发未认证连接数
MaxStartups 10:30:60

# 设置登录超时
LoginGraceTime 30

# 禁用 X11 转发(服务器通常不需要)
X11Forwarding no

# 禁用不安全的认证方式
KbdInteractiveAuthentication no

# 显示上次登录信息
PrintLastLog yes

# 客户端存活检测
ClientAliveInterval 300
ClientAliveCountMax 2

# 仅允许特定用户登录
AllowUsers ubuntu deploy

# 或仅允许特定组
# AllowGroups sshusers
# 检查配置语法
sudo sshd -t
# 重新加载配置(不断开现有连接)
sudo systemctl reload ssh使用 Drop-in 配置
Ubuntu 26.04 支持在 /etc/ssh/sshd_config.d/ 中添加独立配置文件:
# 创建自定义配置
sudo tee /etc/ssh/sshd_config.d/hardening.conf << 'EOF'
PermitRootLogin no
PasswordAuthentication no
MaxAuthTries 3
X11Forwarding no
EOF

sudo systemctl reload ssh
常用 SSH 操作
基本连接
# 基本连接
ssh user@server-ip

# 指定端口
ssh -p 2222 user@server-ip

# 指定密钥
ssh -i ~/.ssh/id_myserver user@server-ip

# 执行远程命令
ssh user@server-ip "df -h && free -h"

# 以详细模式连接(调试用)
ssh -v user@server-ip
ssh -vvv user@server-ip  # 更详细
文件传输
# SCP:复制文件到远程
scp localfile.txt user@server-ip:/remote/path/

# SCP:从远程复制文件
scp user@server-ip:/remote/file.txt ./local/

# SCP:复制目录
scp -r ./local-dir user@server-ip:/remote/path/

# SFTP:交互式文件传输
sftp user@server-ip

# rsync:增量同步(推荐大量文件)
rsync -avz --progress ./local-dir/ user@server-ip:/remote/dir/
SSH 端口转发
# 本地端口转发:将远程服务映射到本地
# 访问本地 8080 即访问远程 MySQL
ssh -L 8080:localhost:3306 user@server-ip

# 远程端口转发:将本地服务暴露给远程
# 远程机器的 9090 端口将转发到本地 3000
ssh -R 9090:localhost:3000 user@server-ip

# 动态端口转发(SOCKS 代理)
ssh -D 1080 user@server-ip

# 后台运行端口转发
ssh -fNL 8080:localhost:3306 user@server-ip
SSH 跳板机
# 通过跳板机连接目标服务器
ssh -J jump-user@jump-host target-user@target-host

# 多级跳转
ssh -J user1@jump1,user2@jump2 user@target
密钥权限要求
SSH 对文件权限有严格要求:
# 正确的权限设置
chmod 700 ~/.ssh
chmod 600 ~/.ssh/id_ed25519          # 私钥
chmod 644 ~/.ssh/id_ed25519.pub      # 公钥
chmod 600 ~/.ssh/authorized_keys     # 授权密钥
chmod 600 ~/.ssh/config              # 客户端配置
防暴力破解
使用 fail2ban
# 安装 fail2ban
sudo apt install fail2ban -y

# 创建本地配置
sudo tee /etc/fail2ban/jail.local << 'EOF'
[sshd]
enabled = true
port = ssh
filter = sshd
logpath = /var/log/auth.log
maxretry = 3
bantime = 3600
findtime = 600
EOF

# 启动服务
sudo systemctl enable --now fail2ban

# 查看封禁状态
sudo fail2ban-client status sshd

# 手动解封 IP
sudo fail2ban-client set sshd unbanip 1.2.3.4
使用 UFW 限制 SSH 访问
# 仅允许特定 IP 访问 SSH
sudo ufw allow from 192.168.1.0/24 to any port 22

# 限制连接频率(30 秒内最多 6 次连接)
sudo ufw limit ssh
故障排查
# 查看 SSH 服务日志
sudo journalctl -u ssh -f

# 查看认证日志
sudo tail -f /var/log/auth.log

# 测试连接(详细模式)
ssh -vvv user@server-ip

# 检查服务端配置是否正确
sudo sshd -t

# 检查 authorized_keys 文件
cat ~/.ssh/authorized_keys

# 检查 SELinux/AppArmor 是否阻止连接
sudo aa-status
常见问题
“Permission denied (publickey)”
# 检查客户端密钥是否正确
ssh-add -l

# 检查服务端 authorized_keys 权限
ls -la ~/.ssh/
ls -la ~/.ssh/authorized_keys

# 确认 sshd_config 中启用了公钥认证
grep PubkeyAuthentication /etc/ssh/sshd_config
“Connection refused”
# 检查 SSH 服务是否运行
sudo systemctl status ssh

# 检查端口是否正确
ss -tlnp | grep ssh

# 检查防火墙
sudo ufw status
“Host key verification failed”
# 删除旧的主机密钥
ssh-keygen -R server-ip

# 或编辑 known_hosts 文件删除对应行
nano ~/.ssh/known_hosts
Last updated on